Isolated database per customer
Every customer runs in a separate database. Companies and projects within a holding share that customer database and are separated by role and project permissions.
Security
Security and infrastructure information in one place
The Reper Ops trust center shares verified information on hosting, isolation, access, backups, sub-processors and security reporting. Contact us with your questions.
Overall availability and outage information is updated on the public status page.
Every customer runs in a separate database. Companies and projects within a holding share that customer database and are separated by role and project permissions.
Production runs in a data center in Frankfurt, Germany; encrypted backup copies are kept in a separate EU country, in Helsinki. The infrastructure provider is ISO/IEC 27001 certified; Reper Ops does not hold its own ISO 27001 certificate.
All access requires HTTPS, TLS 1.2 or higher and HSTS.
The live database and its backups are kept on encrypted disks; the application server reaches the database only over a private network with an encrypted connection. Uploaded documents, photos and on-server backups are also kept on encrypted disks.
Role-based permissions work together with project and unit scope and module licensing. Every user can use two-step verification with an authenticator app; customer administrators can require it for admins or for all users. Sessions refresh when permissions change.
Who changed what and when is recorded; Excel and PDF exports are logged too. Default retention is 180 days and the customer can extend up to 10 years. Advanced query and export screens are in the Analytics and Audit package.
Content security policy and security headers are applied. Every release passes automated checks before going live: authorization and scope rule audit, dependency vulnerability scanning, secret scanning and an API smoke test. Updates are deployed with zero downtime. An independent penetration test is planned.
Modules disabled in the license do not appear in the menu. An enabled module can be narrowed further with role-based exceptions.
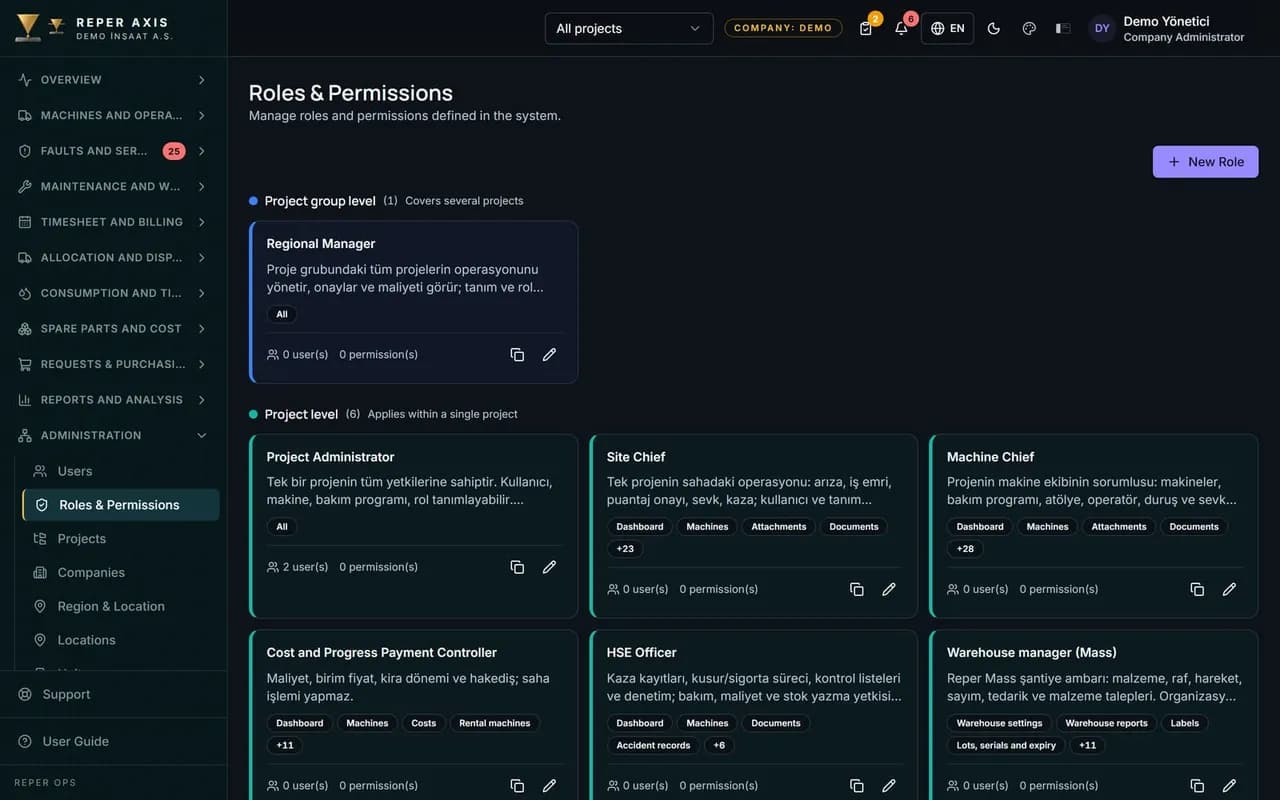
Who changed what and when, kept on the record
Hourly
Database backup, kept for 48 hours
90 days
Encrypted off-site copy
≤ 1 hour
Data-loss target on database failure
30 min
Single-customer restore target
In the October 2026 restore drill the databases were restored successfully from both on-server and encrypted off-site copies.
The system is measured regularly with staged load tests that mimic real field usage; before major infrastructure changes, the test is repeated on the current version.
Each customer’s concurrent workload is protected by separate limits; one customer’s heavy usage does not slow down other customers.
Under extreme load, field records (faults, meter readings, QR code entries) take priority; heavy reports are briefly deferred and no data is lost.
Large Excel and PDF exports are prepared in the background; the user is notified when they are ready, so the screen never has to wait.
When the connection drops, field entries are queued on the device and sent once the connection returns, exactly once and without creating duplicate records.
Every layer has timeout limits; a single stuck operation cannot lock up the system.
New versions are released without downtime: the new version starts alongside the old one, and traffic is not switched to it until it has passed health checks and automated security tests.
Capacity, latency and error rates are monitored continuously; when a threshold is exceeded, the team is alerted automatically.
The providers below are used only for the stated purposes. Google Analytics and LinkedIn Insight are used only on the marketing website with cookie consent and never inside the application.
| Service | Purpose |
|---|---|
| Hosting infrastructure | Application, database and encrypted backup storage; within the European Union |
| Email service | Transactional email (notifications, password reset) |
| Mobile notification service | Push notifications to the mobile app |
| WhatsApp notification service | WhatsApp notifications; only if the customer enables them |
| Error monitoring service | Application error monitoring; within the European Union |
| AI service | AI features; only if the customer enables them, with the provider and data location disclosed beforehand |
| Machine manufacturer telematics portals | Machine data pulled when the customer connects their own manufacturer account |
Good-faith researchers who report issues within these rules will not face legal action from Reper Ops. First response target is 5 business days. Report to: guvenlik@reperops.com
Security summary, named sub-processor list and enterprise security questionnaire answers are shared on request. Use the contact form for detailed questions.
No. Each customer runs in its own database. Companies and projects within a holding share that customer database and are separated by role and project permissions.
Yes. Critical actions and Excel and PDF exports are written to the audit trail. Default retention is 180 days; the customer can extend up to 10 years.
Yes. A subdomain with your company name or a domain owned by your company can be used. On-premises or customer-cloud requests are evaluated case by case; contact us.
Yes. Every user can use two-step verification with an authenticator app on the web and in the mobile app. Customer administrators can require it for admins or for all users.
The database is backed up hourly on the server and kept for 48 hours; daily encrypted off-site copies are kept for 90 days. The database service also supports restoring to any point within the last 15 days. In the October 2026 drill the databases were restored from both sources. Target maximum data loss is 1 hour for a database failure and 24 hours if the entire server is lost.
Production data is hosted in a data center in Frankfurt, Germany; encrypted backup copies are kept in Helsinki, Finland. All data stays within the European Union. Personal data processing and privacy texts are on the privacy and data protection (KVKK) page on this site.
No independent penetration test has been completed yet; an independent penetration test is planned.
Take the first step toward a more efficient, more controlled and more profitable operation.